Information Security
- Information Security Organization
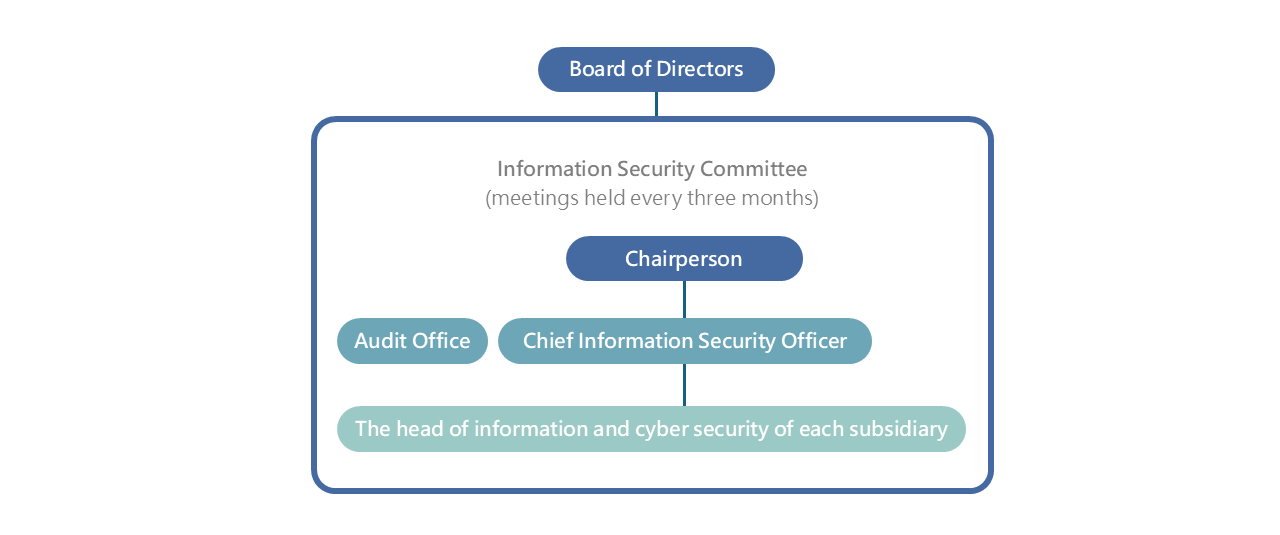
SAS established its Information Security Committee in March 2023. The committee members are comprised of the highest-ranking information or information security officers from the company’s subsidiaries. Since its inception, the committee has convened biannually, but starting from December 2024, meetings will be held quarterly. The committee aims to coordinate the formulation, implementation, risk management, and compliance of policies related to information security.
To integrate information security management policies and risk management into daily operations, SAS also requires each subsidiary within the group to establish its own Information Security Task Force. Members of these task forces are representatives from various departments, who discuss and communicate information security matters relevant to their departmental operations during meetings. They are responsible for implementing the information security policies and practices set forth by the Information Security Committee.
Additionally, SAS incorporates information security into performance evaluations. The Information Security Office at SAS headquarters tracks the performance indicators of information security implementation at all group locations on a monthly basis. Based on operational needs, it provides information security goals, improvement guidelines, and necessary resource support to help achieve the group’s overall information security objectives. Departments are also required to implement the resolutions of the Information Security Committee, share experiences in improving information security, establish a group-wide joint defense mechanism, and enhance the overall information security framework.
- Information Security Governance and Continuous Improvement
SAS has established an information security policy and information security management procedures, utilizing the PDCA (Plan, Do, Check, Act) cycle to ensure the achievement of established goals and continuous improvement.
Security Testing
Data Protection Measures
Personnel Management
Network Security Protection
Security testing is regularly implemented, including host vulnerability scanning and system updates.
Data protection measures. Regular backups and proper storage, management of external information storage media, minimization of access privileges, account and password complexity restrictions, etc.
Regular training for employees, periodic information security awareness campaigns, supplier access management, and regular social engineering drills.
Firewall rule reviews, secure remote connections, realtime monitoring of traffic and anomalies, and regular operational continuity drills.
- Information security knowledge and awareness training
- Information Security Managers and Information Security Officers of all subsidiaries convene Information Security Committee meetings on a quarterly basis.
All employees are required to participate in information security awareness and training programs annually. In 2025, each employee completed at least two information security-related training courses. - Each dedicated information security professional (currently two designated information security personnel) completed an average of 30 hours of professional information security training during 2025.
- The vulnerability scanning and monitoring score for externally facing systems achieved a rating of 96 points.
- The Company engaged a professional cybersecurity service provider to conduct Red Team exercises to enhance its ability to detect, respond to, and defend against potential cyberattacks.
- Information security KPIs are established and periodically audited by the Information Security Committee to enhance the organization’s cybersecurity maturity. In 2025, 100% implementation of three key indicators was achieved across all subsidiaries.
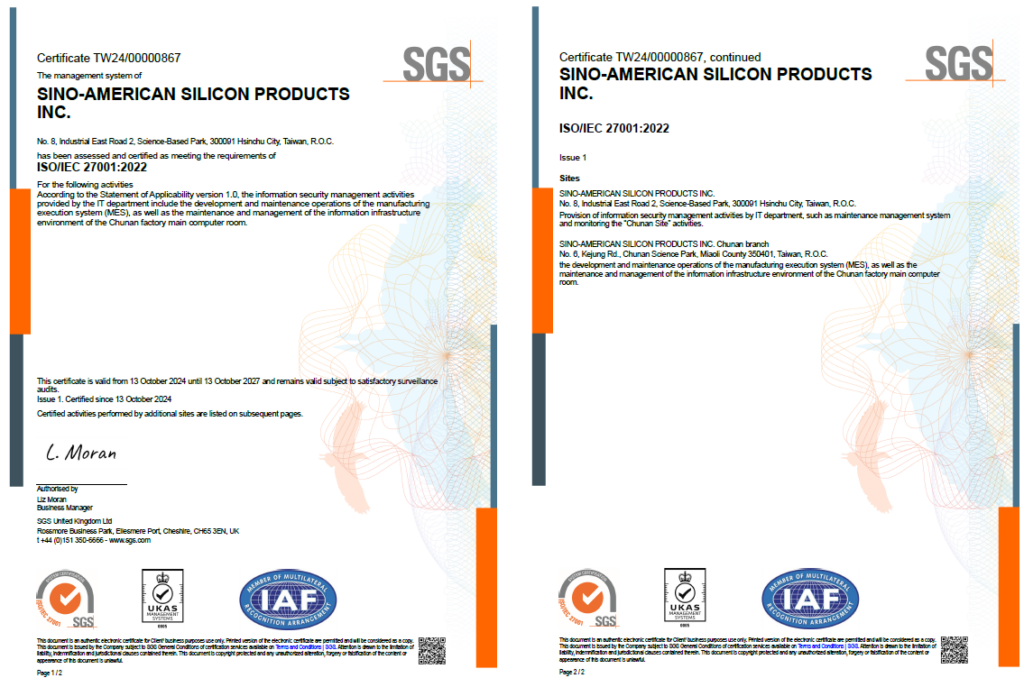
- ISO 27001 Certification
SAS implement Information security management system (ISO 27001). We actively enforce to improve the performance of ISMS to ensure the effectiveness management system of ISMS.